Investigation Lab: Make the right call, faster

Get a trusted second opinion on suspicious files and indicators. Use IOC Search and deep sandbox analysis to reduce uncertainty, accelerate investigations and make confident decisions.

Why a second opinion matters

Conflicting verdicts

Different tools can return different answers, leaving analysts to determine which verdict to trust and slowing down response.

Indicators lacking context

A simple verdict can be indicative but rarely tells the whole story. To ensure elevated security posture and fast response, teams need deeper evidence and context.

Sample privacy

Submitting files for external analysis can expose sensitive samples. Security teams need credible insights without compromising privacy.

Turn uncertainty into confident action

Get reliable evidence backed by ESET's global telemetry, decades of threat research experience and internal analysis infrastructure. Reduce uncertainty and make informed decisions without exposing sensitive samples. 

GAIN CONFIDENCE

Validate suspicious activity against ESET’s proprietary telemetry and threat intelligence for a credible second opinion.

DECIDE FASTER

Move quickly from IOC enrichment to deeper behavioral analysis, helping you get the evidence for the right response sooner.

CUT THROUGH THE NOISE

ESET experts curate and review findings to ensure confirmed indicators are always precise, relevant and ready for action.

KEEP THINGS PRIVATE

Analyze suspicious files without unnecessarily exposing sensitive samples or investigation details.

How it works

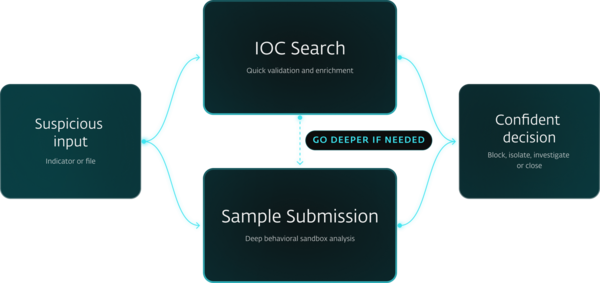
Integrate ESET Threat Intelligence Investigation Lab into your existing stack through APIs or use it manually. When external alerts from your SIEM, SOAR, XDR or TIP require validation, use IOC Search to quickly assess suspicious indicators against ESET telemetry, then submit priority files for deeper behavioral analysis when needed. Based on the outcome, make an informed, confident decision whether to block, investigate, escalate or close.
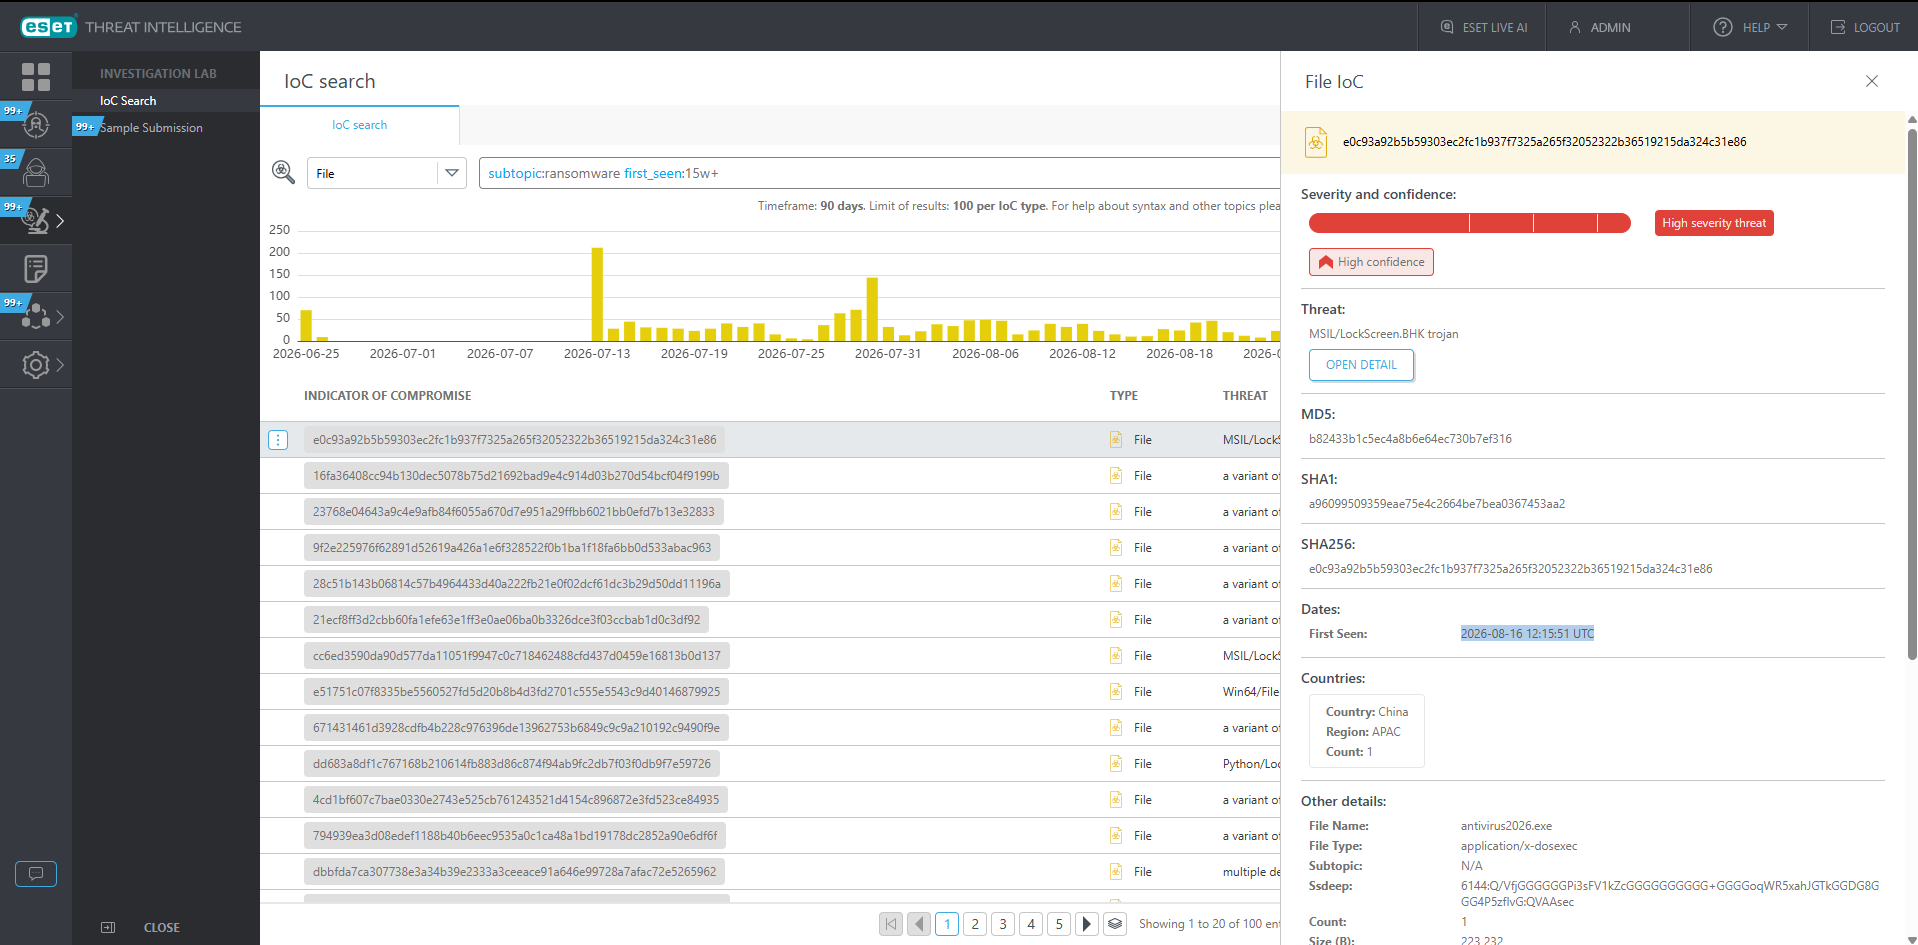
IOC Search

Search suspicious indicators against ESET telemetry and reputation data to quickly enrich alerts, triage large volumes and determine what deserves further investigation.
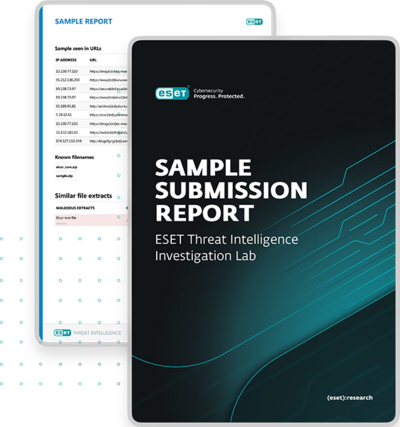
Sample Submission

Submit suspicious files for in-depth sandbox analysis to uncover behavioral evidence and get readable, analyst-friendly insights without maintaining additional infrastructure.

Choose the right fit for your SOC

Investigation Lab

Investigation Lab Advanced

Best suited for

Teams needing reliable IOC enrichment and occasional deep file analysis

Teams with higher investigation volumes and advanced analysis needs

Full API Access

  • Yes​
  • Yes​

IoC Search (botnets, C&Cs, domains, IPs, URLs)

1,000/day; 5,000/week

10,000/day; 50,000/week

Advanced querying across ESET database

  • Yes​
  • Yes​

Sample Submission

50/day; 250/week

500/day; 2,500/week

In-depth behavioral analysis

  • Yes​
  • Yes​

Sandbox customization​

  • No
  • Yes​

Sandbox processing priority​

Standard​

High​

Sample privacy

Standard — sample deleted;
verdict and hash retained

High — sample,
verdict and hash deleted
Expand your Threat Intelligence coverage

APT Reports

With millions of sensors and strong visibility into hard-to-see regions, ESET delivers clear insight into global and emerging cyber threats.

eCrime Reports

Clear, actionable intelligence on financially motivated cybercrime operations and malware ecosystems.

Feeds

Real-time, curated data streams built for automation and integration.

Stay informed. Stay ahead

THE LATEST ESET THREAT REPORT

An in-depth look at global threat trends, regional APT activity and malware developments observed through ESET telemetry.

APT Activity Summary

Latest insights into active APT campaigns across the globe.

WeLiveSecurity: Top stories and research

Expert analysis and commentary from ESET researchers on the latest cyber threats, discoveries and security trends.

ESET Research Podcast: Exploring the global threat landscape

Join our analysts as they discuss attribution, tooling and global activity shifts

Investigation Lab Overview

Explore key benefits, analysis workflow and service tiers.

Frequently Asked Questions

What is Investigation Lab?

Investigation Lab is an analyst-focused investigation service that combines IOC Search and deep sandbox analysis to help security teams validate suspicious indicators and files. It provides a trusted second opinion backed by ESET telemetry, reputation intelligence and behavioral evidence, enabling faster and more confident response decisions.

Can I use IOC Search without submitting a file?

Yes. IOC Search and Sample Submission can be used independently. You can look up IP addresses, domains, URLs, hashes and other indicators to gain additional context without uploading a sample for analysis.  

Are submitted samples shared publicly?

No. Submitted samples are never published to public malware-sharing communities. Sample retention and handling depend on the selected access mode and service tier, with enhanced privacy options available in higher tiers.

Does Investigation Lab replace a threat intelligence platform?

No. Investigation Lab is designed to complement your existing security and threat intelligence workflows. It provides additional validation, enrichment and behavioral analysis to help analysts make better-informed decisions, rather than replacing a broader security stack or threat intelligence platform.

What types of indicators can I search?

IOC Search supports common indicators used in security investigations, including domains, IP addresses, URLs, botnets, command-and-control (C&C) infrastructure and other threat-related artifacts. Results help enrich alerts, accelerate triage and identify activity that requires deeper analysis.

When should I submit a file for sandbox analysis?

File submission is ideal when IOC enrichment alone does not provide sufficient context or when you need deeper insight into a file's behavior. Sandbox analysis helps uncover malicious activity, execution chains, network communication and other behavioral indicators that support informed decision-making.

How can I integrate Investigation Lab into my existing workflows?

Investigation Lab can be used manually through the user interface or integrated into existing SOC workflows through APIs. This allows security teams to enrich alerts directly within SIEM, SOAR, XDR and TIP platforms, helping automate investigations and accelerate response.

LET’S CONNECT

Curious to learn more? Share your contact details and we’ll follow up with more information. 
We can walk you through a demo, discuss a proof of concept or answer any questions you may have.